

Alkira’s Network Infrastructure-as-a-Service (NIaaS) platform helps businesses to extend their on-prem networks into Google cloud and also extend into hybrid multi-cloud networks from GCP.
Google Cloud Platform (GCP) offers unique networking capabilities compared to other cloud providers. Unlike traditional cloud networking models, GCP’s Virtual Private Cloud (VPC) spans multiple regions, whereas similar constructs in other cloud platforms are typically confined to a single region. Additionally, when launching an instance in GCP, its multiple network interfaces cannot belong to the same VPC. This means that if a virtual machine (VM) or firewall appliance needs multiple interfaces for different traffic flows, each NIC must be attached to a different VPC. These distinctions can introduce challenges for enterprises migrating to GCP or embarking on their cloud adoption journey. Alkira simplifies these complexities by providing a seamless, cloud-native network infrastructure on-demand solution.
In this blog, we will explore Alkira’s capabilities in GCP, demonstrating how it integrates with various connectivity options. We will also discuss key customer requirements for each option and demonstrate how Alkira simplifies, streamlines cloud networking, and meets customer requirements effortlessly.
Extending On-prem Connectivity to GCP VPC
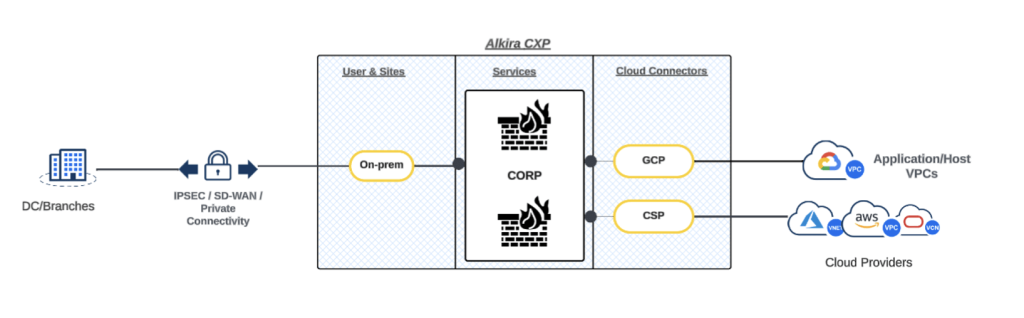
Customers can onboard their application/host VPCs directly onto the Alkira Cloud Exchange Point (CXP), establishing secure Cloud attachments for connectivity. With Alkira managing both routing and connectivity, all VPC subnets can be advertised to:
- Other GCP VPCs
- Cloud environments (AWS, Azure, etc.)
- On-premises networks connected to Alkira CXP
For VPCs with existing connectivity, routing can be selectively managed using either a default route or specific prefix-based routing to maintain granular traffic control.
Extending On-prem Connectivity to GCP Global VPC

Global VPC spans multiple regions, making routing across different environments complex. Alkira simplifies this by enabling seamless connectivity to the Global VPC, ensuring dynamic failover across regions and traffic symmetry within each region. By leveraging BGP Multi-Exit Discriminator (MED) values, Alkira optimizes route selection, path preference, and failover handling for a more efficient and resilient network.
Extending On-prem Connectivity to GCP VPC with Private Service Connect
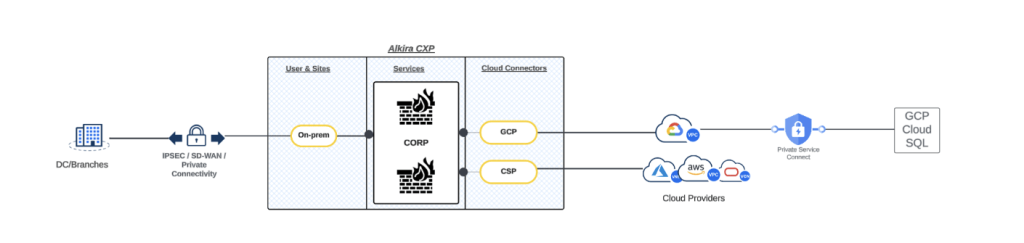
GCP Private Service Connect enables private connectivity to:
- Native GCP services
- Services hosted in other GCP accounts
- Marketplace services from third-party providers
To leverage this, customers create Private Service Connect endpoints to establish connectivity with these services. Once the VPC with endpoints is onboarded to Alkira CXP, Alkira extends these services to other cloud providers or on-prem environments without the need for manual route management. This ensures secure and scalable multi-cloud connectivity and the ability to access these services privately from the on-prem environments.
Extending Private Connectivity using GCP Interconnect
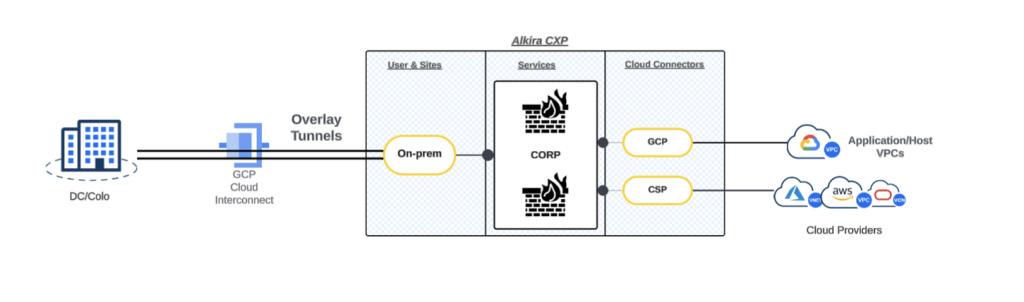
For high-bandwidth private connectivity into GCP, customers can use GCP Interconnect via Alkira CXP. The process is straightforward:
- Use the Alkira portal to provision the Interconnect Connector.
- Once provisioned, Alkira generates the Pairing Key to the onboard circuit on the Colo.
- Terminate the Interconnect in Alkira’s GCP account.
- Configuration will be available on Alkira portal to download.
- Establish underlay peering between the on-premises/colo router and GCP.
- Configure the Overlay between Alkira and Colo Router.
Beyond private connectivity, Alkira extends this connection to workloads across multiple clouds and GCP regions, since an overlay is created which enables a unified, scalable, and flexible cloud networking experience.
Another benefit of using Alkira to extend private connectivity into GCP is that when a customer has different route domains or VRFS in their on-premise environment and they want to extend these into the GCP, Alkira can use the same GCP Interconnect as an underlay and have different overlay tunnels which will be part of a different segment. Customers can then easily extend different VRFs to GCP or to the other cloud environments.
Internet Ingress and Egress Traffic in GCP
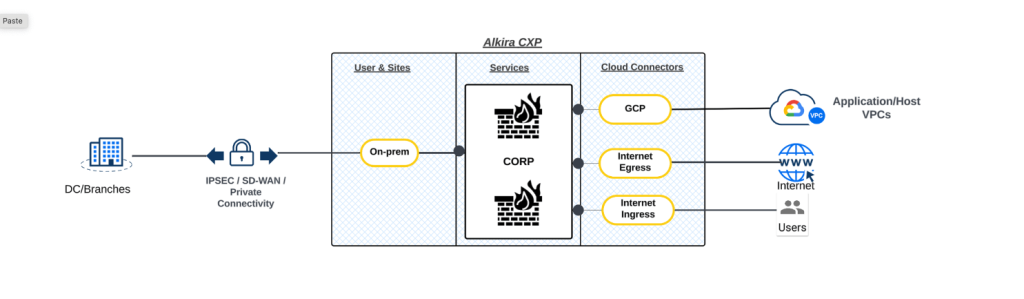
Figure 5: Internet Egress and Ingress Connectivity into GCP using Alkira CXP
Alkira’s Internet Facing Application (IFA) streamlines application connectivity in Google Cloud Platform (GCP) by eliminating the need for external load balancers, manual NAT configurations, and complex VPC peering. Traditionally, GCP applications require load balancers to route and distribute traffic, adding cost and operational overhead. With Alkira IFA, applications seamlessly connect across VPCs, regions, and even multi-cloud environments—without additional infrastructure.
For internet egress, Alkira enables a centralized breakout via the Cloud Exchange Point (CXP), ensuring all workloads share a consistent egress IP. This enhances security, simplifies policy enforcement, and removes the need for complex routing configurations, providing a cost-effective, scalable, and secure solution for GCP networking.
Benefits of Alkira
Segmentation
Alkira segments create unique routing and policy spaces, ensuring seamless isolation for workloads and traffic flows. Each segment maintains its own routing and policies, allowing customers to easily enforce traffic restrictions. GCP workloads can be onboarded into different segments based on specific routing requirements, enhancing security and control.

Manage Overlapping IPs
Alkira provides the ability to configure different NAT policies to overcome any overlapping IPs in the customer environment. For example, if multiple GCP VPCs have the same IP address configured NAT configurations can be applied on the Alkira CXP without adding any additional agents or firewalls on the GCP side which would be the case in a cloud native environment.
Visibility and Troubleshooting
Alkira provides robust monitoring and visibility into all traffic traversing cloud workloads in GCP. Users gain detailed insights into traffic types, direction, and bandwidth utilization, facilitating efficient troubleshooting and network optimization.
Automation with Terraform
Deploying network infrastructure at scale requires automation, and Alkira streamlines this process with Terraform integration. Customers can use a single Terraform provider to provision Alkira network infrastructure across GCP regions, on-prem environments, or other cloud providers, enabling consistent and efficient deployments.
Conclusion
Whether you are looking to scale up your GCP deployment or move into multiple cloud providers Alkira can provide you with the capabilities and the connectivity without having to deal with any operational burden. Please reach out to us at [email protected] if you like to schedule a demo or discuss the solution in more detail.

Ahmed Abeer